- On-premises
- SaaS
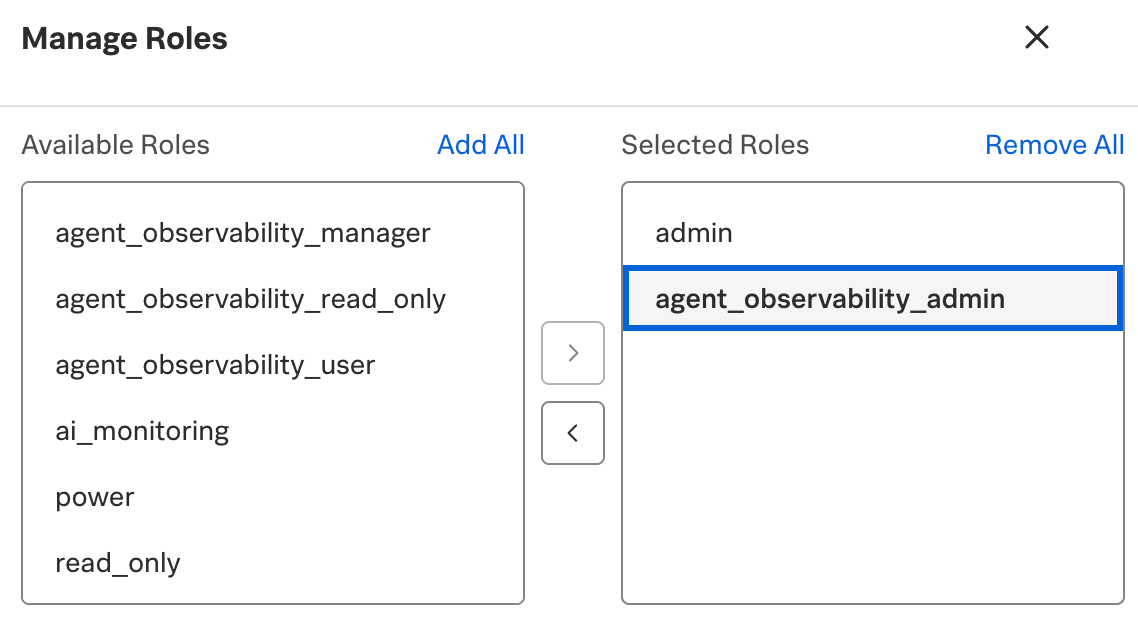
The following sections only apply to on-premises, standalone, and custom deployments of Splunk Agent Observability.The following sections apply to on-premises, standalone, and custom deployments of Splunk Agent Observability.In table form: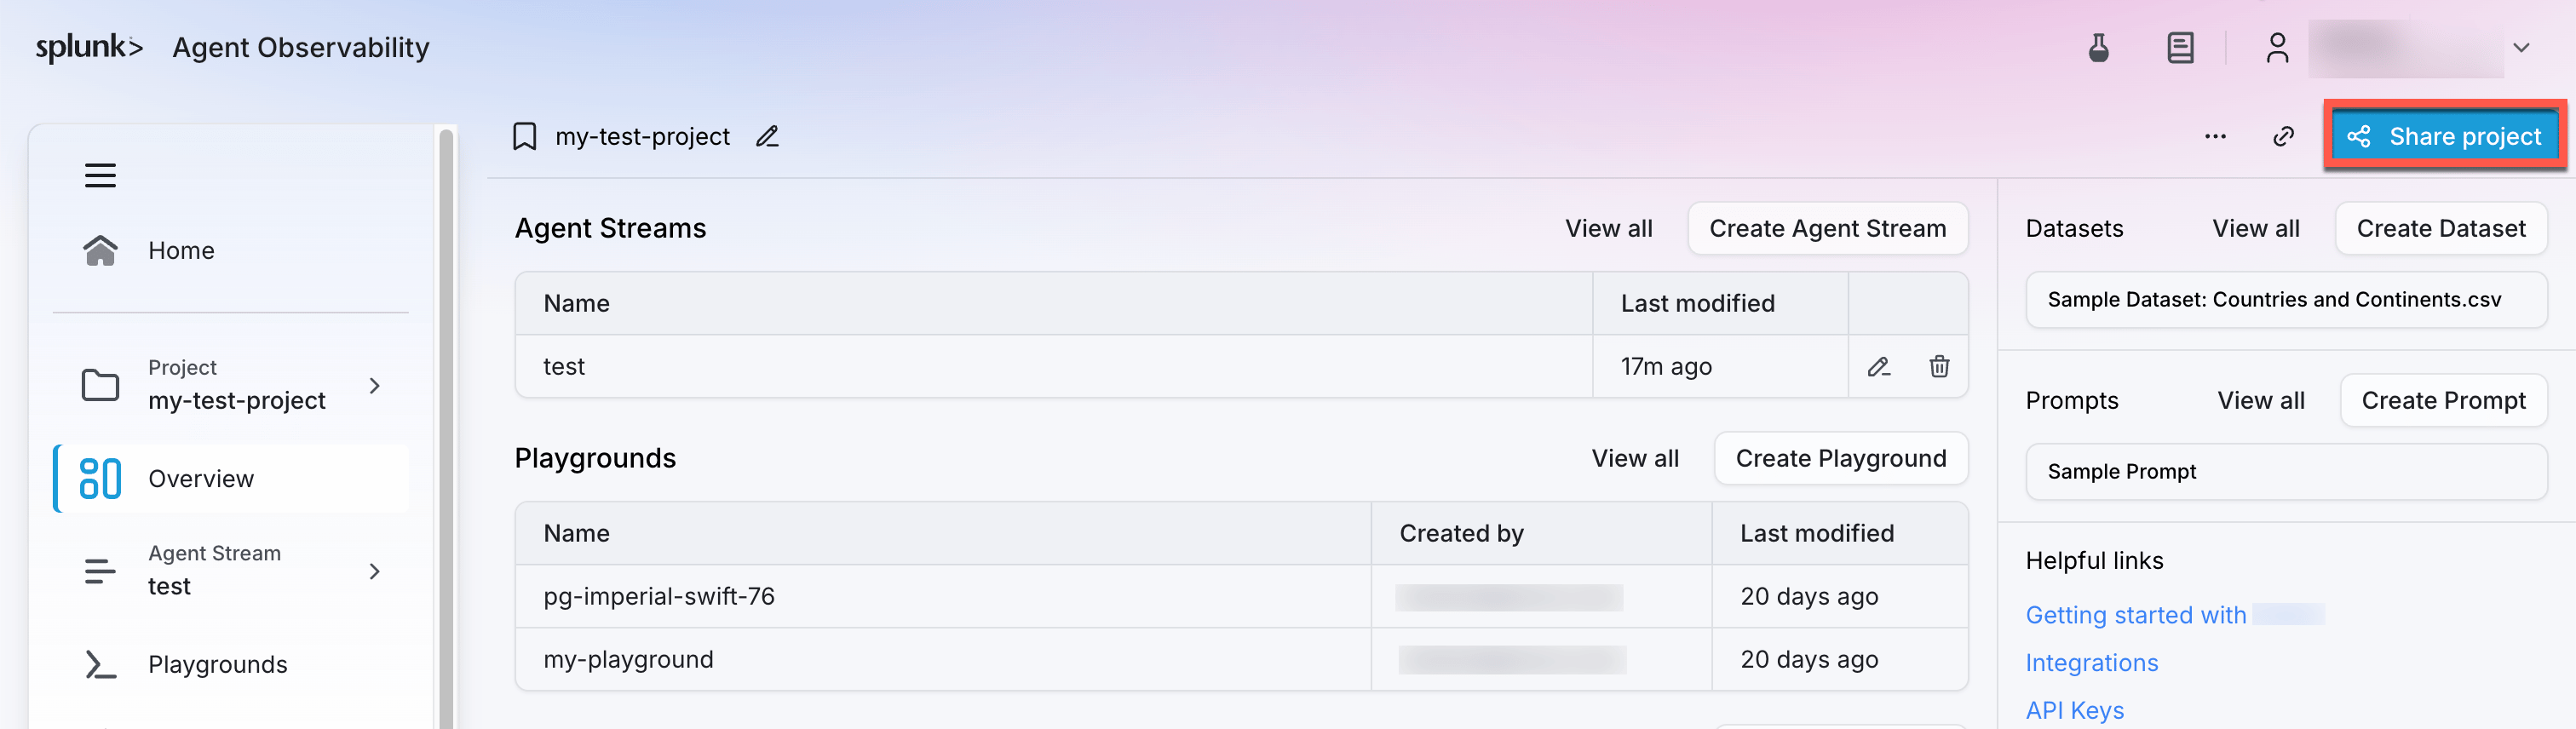
System-level roles (On-premises)
You can assign users the following roles:- Admin: Full access to the organization, including viewing all projects.
- Manager (enterprise only): Can add and remove users.
- User: Can create, update, share, and delete projects and resources within projects.
- Read-only: Cannot create, update, share, or delete any projects or resources. Limited to view-only permissions.
Free users of Splunk Agent Observability can only use the Admin, User, or Read-only roles. Contact us to explore a paid plan and get full RBAC.
Add users to your organization (On-premises)
You must have the admin or manager role to add users to your organization.To send email invitations to users, follow these steps:- Log into Splunk Agent Observability.
-
Select your user profile in the upper-right corner.
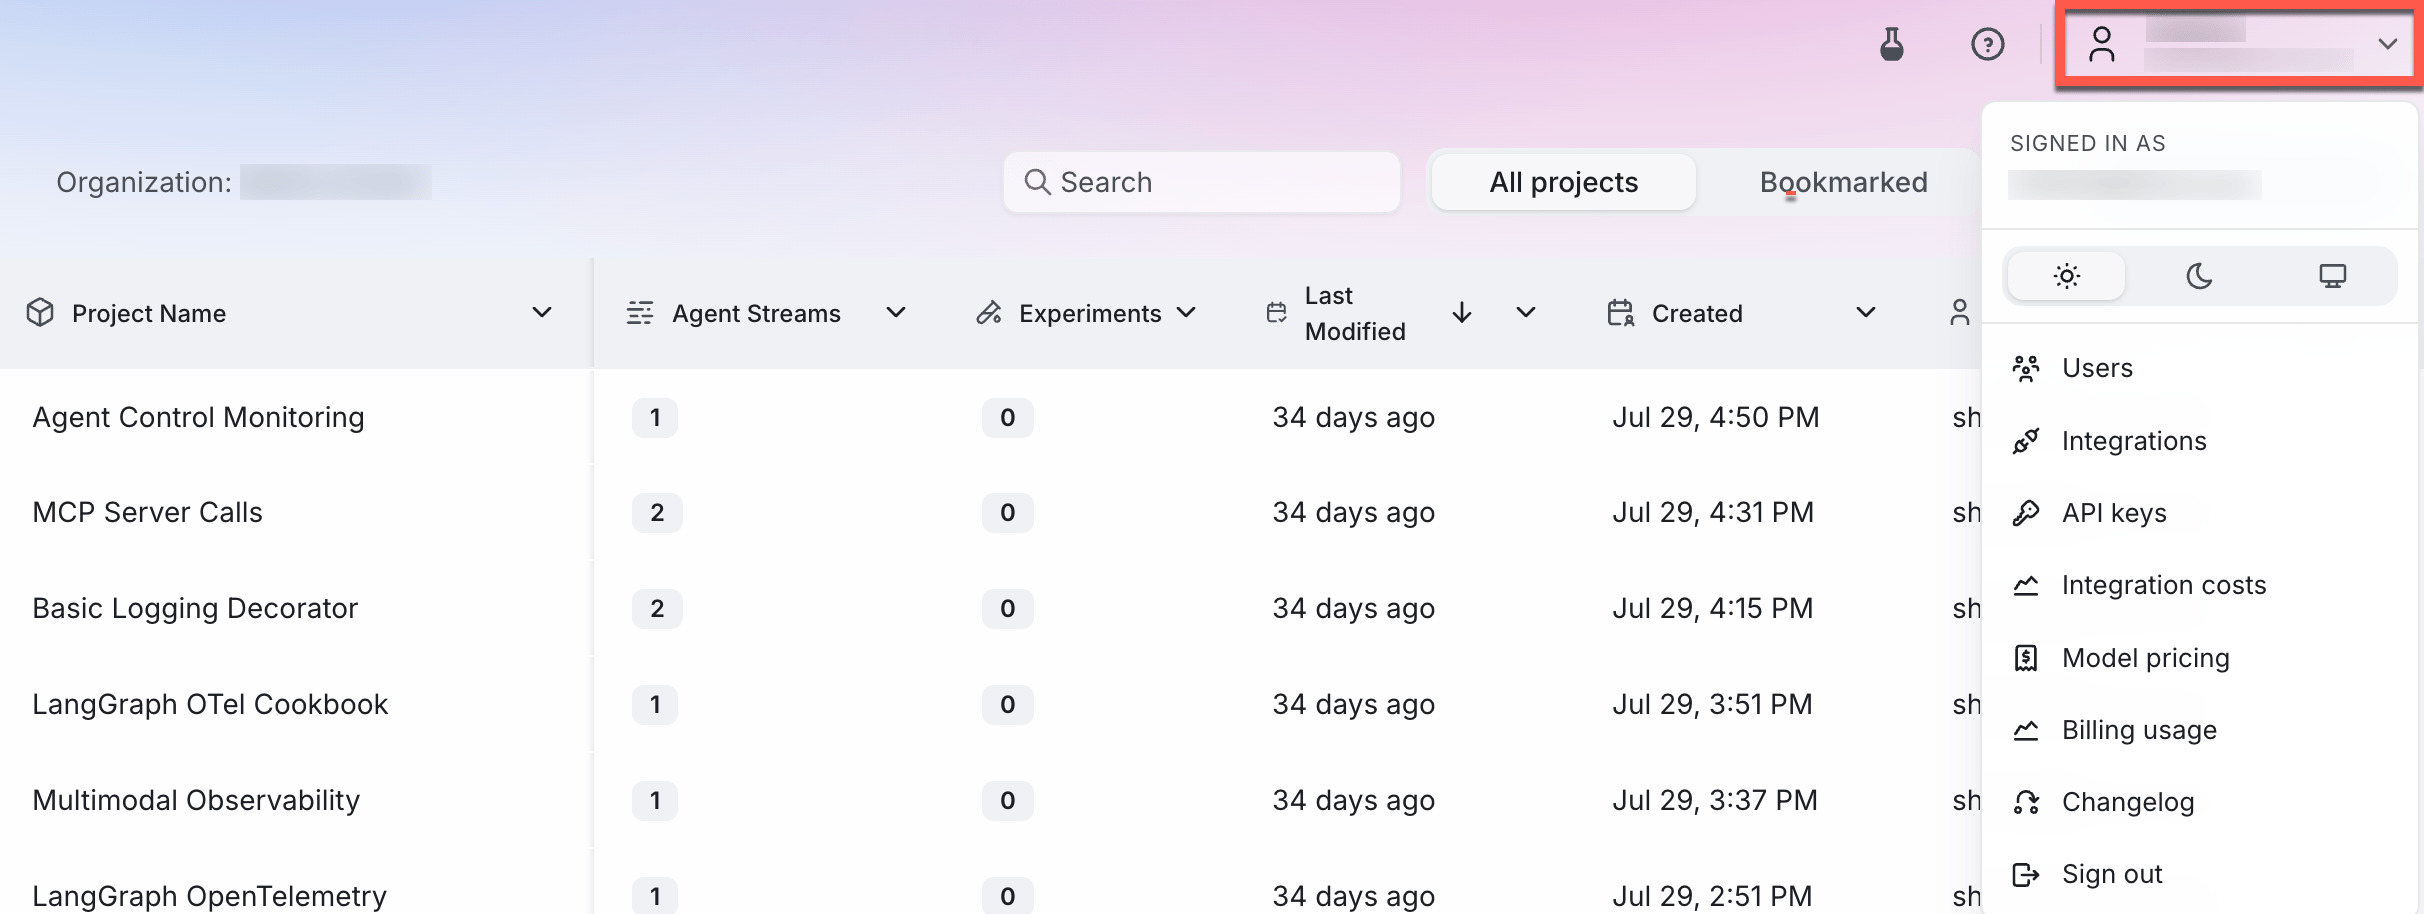
- Select Users.
- Select Invite Users.
- Enter the emails of the users you want to invite and the role you want to assign to them. See System-level roles for more information on roles.
- Select Invite.
Assign roles to users (On-premises)
To assign a role to user who is already part of your organization, follow these steps:- Log into Splunk Agent Observability.
-
Select your user profile in the upper-right corner.
- Select Users.
- Search for the user’s email. In the row for the user, select their Role and choose a new role from the drop-down menu.
Groups (On-premises, enterprise only)
Users can be organized into groups to streamline sharing projects. Currently, groups are only available to customers on paid plans of Splunk Agent Observability.There are 3 types of groups:- Public: Group and members are visible to everyone in the organization. Anyone can join.
- Private: Group is visible to everyone in the organization. Members are kept private. Access is granted by a group maintainer.
- Hidden: Group and its members are hidden from non-members in the organization. Access is granted by a group maintainer.
- Maintainer: Can add and remove members.
- Member: Can view other members and shared projects.
Project sharing (On-premises)
By default, only a project’s creator (and managers and admins) have access to a project. Projects can be shared both with individual users and entire groups. Together, these are called collaborators.To share a project with collaborators, select your project from the main menu. From the project homepage, select Share project.